Blog
Agentic AI Security: MCP OAuth, VPN & HashiCorp Vault Leases
OAuth 2.1 for MCP, private network paths, and short-lived Vault secrets — baselines for Claude, OpenAI, and Cursor
On this page
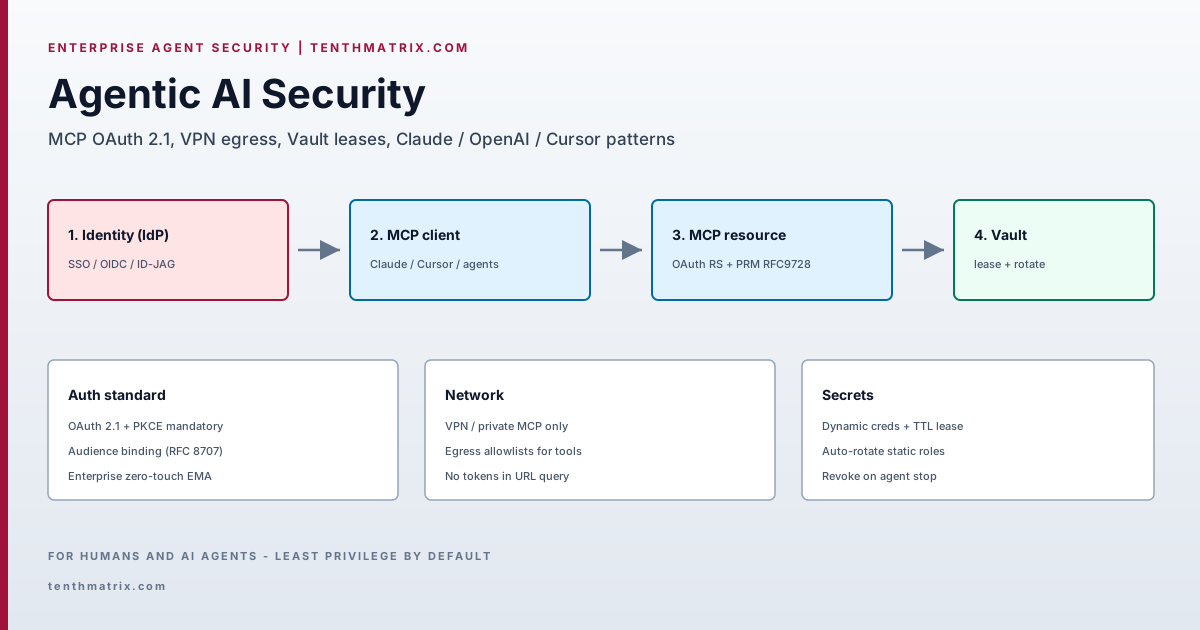
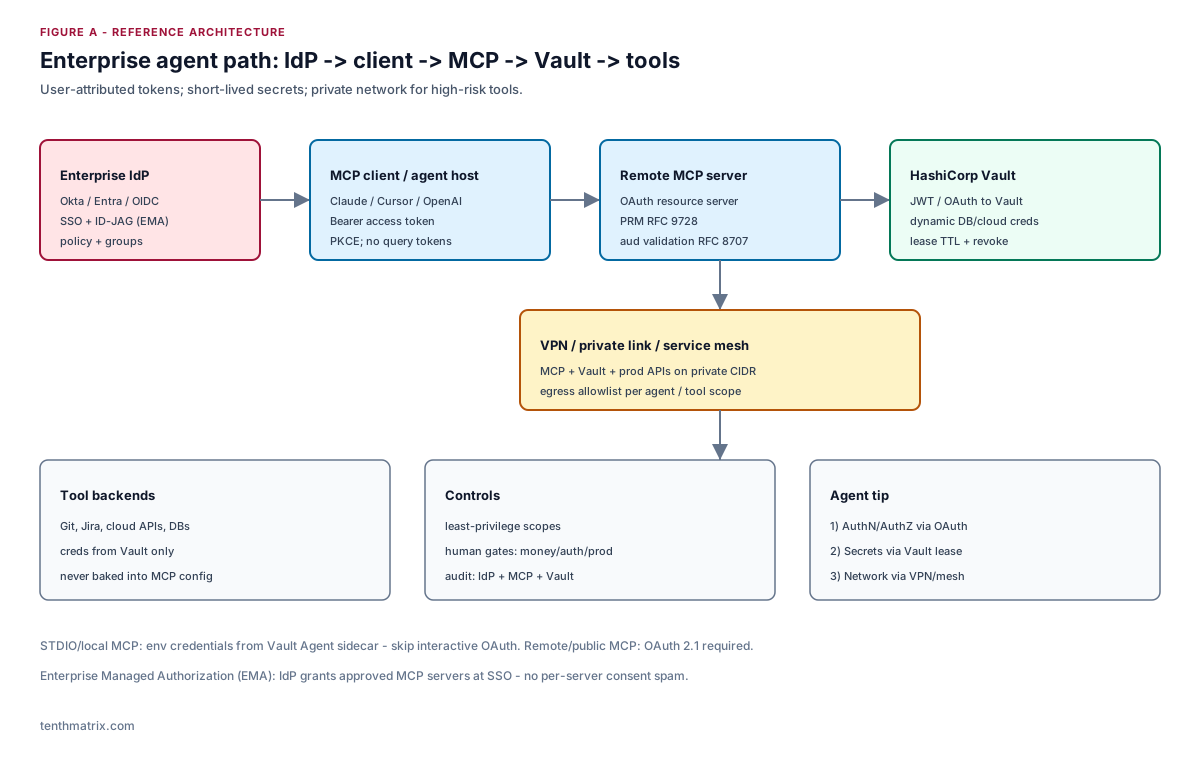
Enterprise agents need three controls that static API keys cannot provide: OAuth-bound MCP access, private network paths (VPN/mesh), and short-lived Vault leases for tool secrets. This digest maps industry baselines for Claude, OpenAI, and Cursor. Full reference architecture in the long article.
Reference path
Vendor baselines (Claude / OpenAI / Cursor)
| Product | Recommended setup |
|---|---|
| Claude | Remote MCP via OAuth; 401 + WWW-Authenticate discovery; never tokens in URL; Vault for tool secrets |
| OpenAI | Isolate model API key; OBO/user-attributed tool tokens; VPC agents; Vault dynamic creds per tool call |
| Cursor | Env-only MCP config; Vault Agent for STDIO; corp VPN to private MCP; team allowlist of servers |
Vault leases (short-lived secrets)
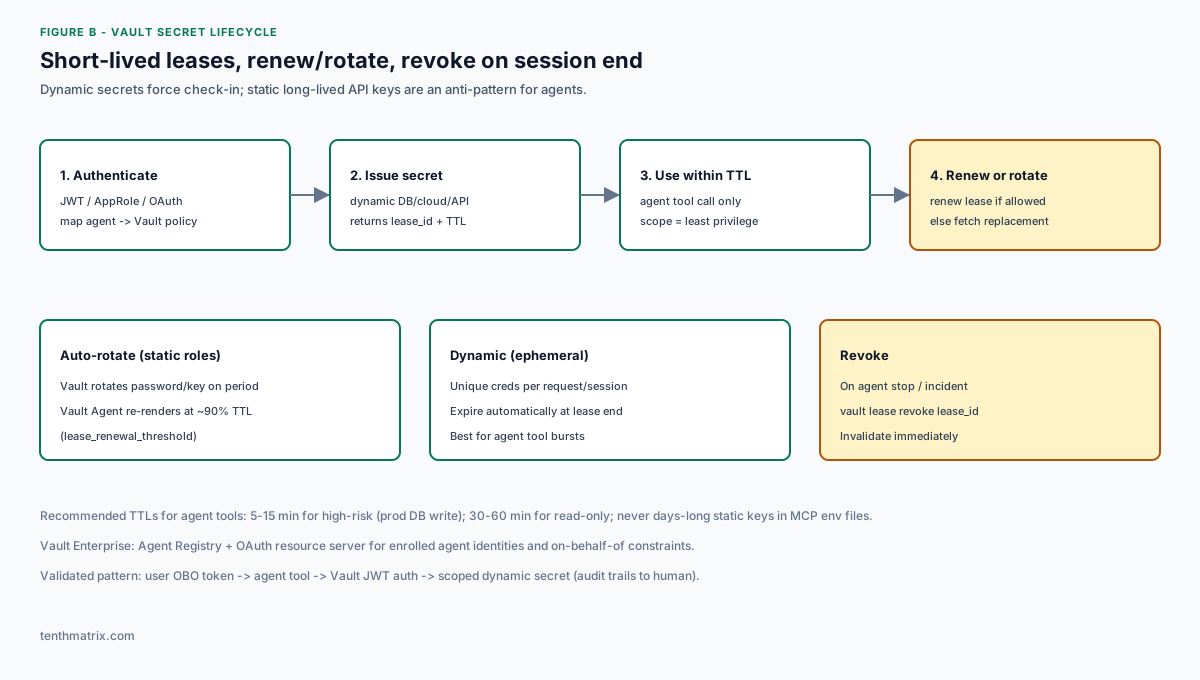
- Dynamic secrets — unique creds +
lease_id+ TTL; expire or revoke when the agent session ends. - Auto-rotate — static roles rotate on a period; Vault Agent refreshes near TTL (default ~90%).
- Enterprise — Agent Registry + OAuth resource server for enrolled agent identities (Vault Enterprise).
TenthMatrix recommendation
Treat MCP OAuth as the front door, VPN as the network door, and Vault as the secret door. Full checklists, RFCs, and anti-patterns: long article.
Published by TenthMatrix.
More from the blog

Observability Is Not Optional: Make It a Business Standard
Why fragmented monitoring creates blind spots, duplicate spend, and slow incidents — and how to make centralised observability a non-negotiable company standard.

WSL Vault for Compliance: One Tenant Never Opens Another’s Secrets
How WSL Vault keeps app, team, and environment tenants cryptographically isolated — so a stolen root-style token cannot empty the estate — and why dual-tenant control beats secrets sprawl.

Workstation AI Shop: Promoting the AI Sales Storefront Through int → test → acc → prod
Workstation AI Shop sells GPU machines with a fully autonomous AI Sales Agent that configures the basket. See how Ring Promoter moves each build through int → test → acc → prod — with Orbit screenshots release engineers and stakeholders share.